Apify rotates API tokens, prompts 2FA resets after breach
Apify has rotated critical internal secrets and revoked some third-party OAuth connections after detecting unauthorized access to its internal systems.
Actualizado hace 1 min
Resumen de 172 notas de ciberseguridad publicadas el 12 de noviembre de 2026. Los temas con más cobertura: vulnerabilidades (60), herramientas e investigación (33), ciberataques y apt (28).
172 notas en castellano e inglés. Quitar filtros
Apify has rotated critical internal secrets and revoked some third-party OAuth connections after detecting unauthorized access to its internal systems.
An active threat campaign is combining port scanning, password guessing, and Transact-SQL (T-SQL) commands to compromise exposed Microsoft SQL servers and deliver malware. The attackers are using predefined username and password lists to brute-force into these servers and…
Microsoft finaliza el soporte de Windows 11 23H2, por lo que los equipos que no actualicen dejarán de recibir parches de seguridad y quedarán vulnerables.
Exploits y PoCVulnerabilidades
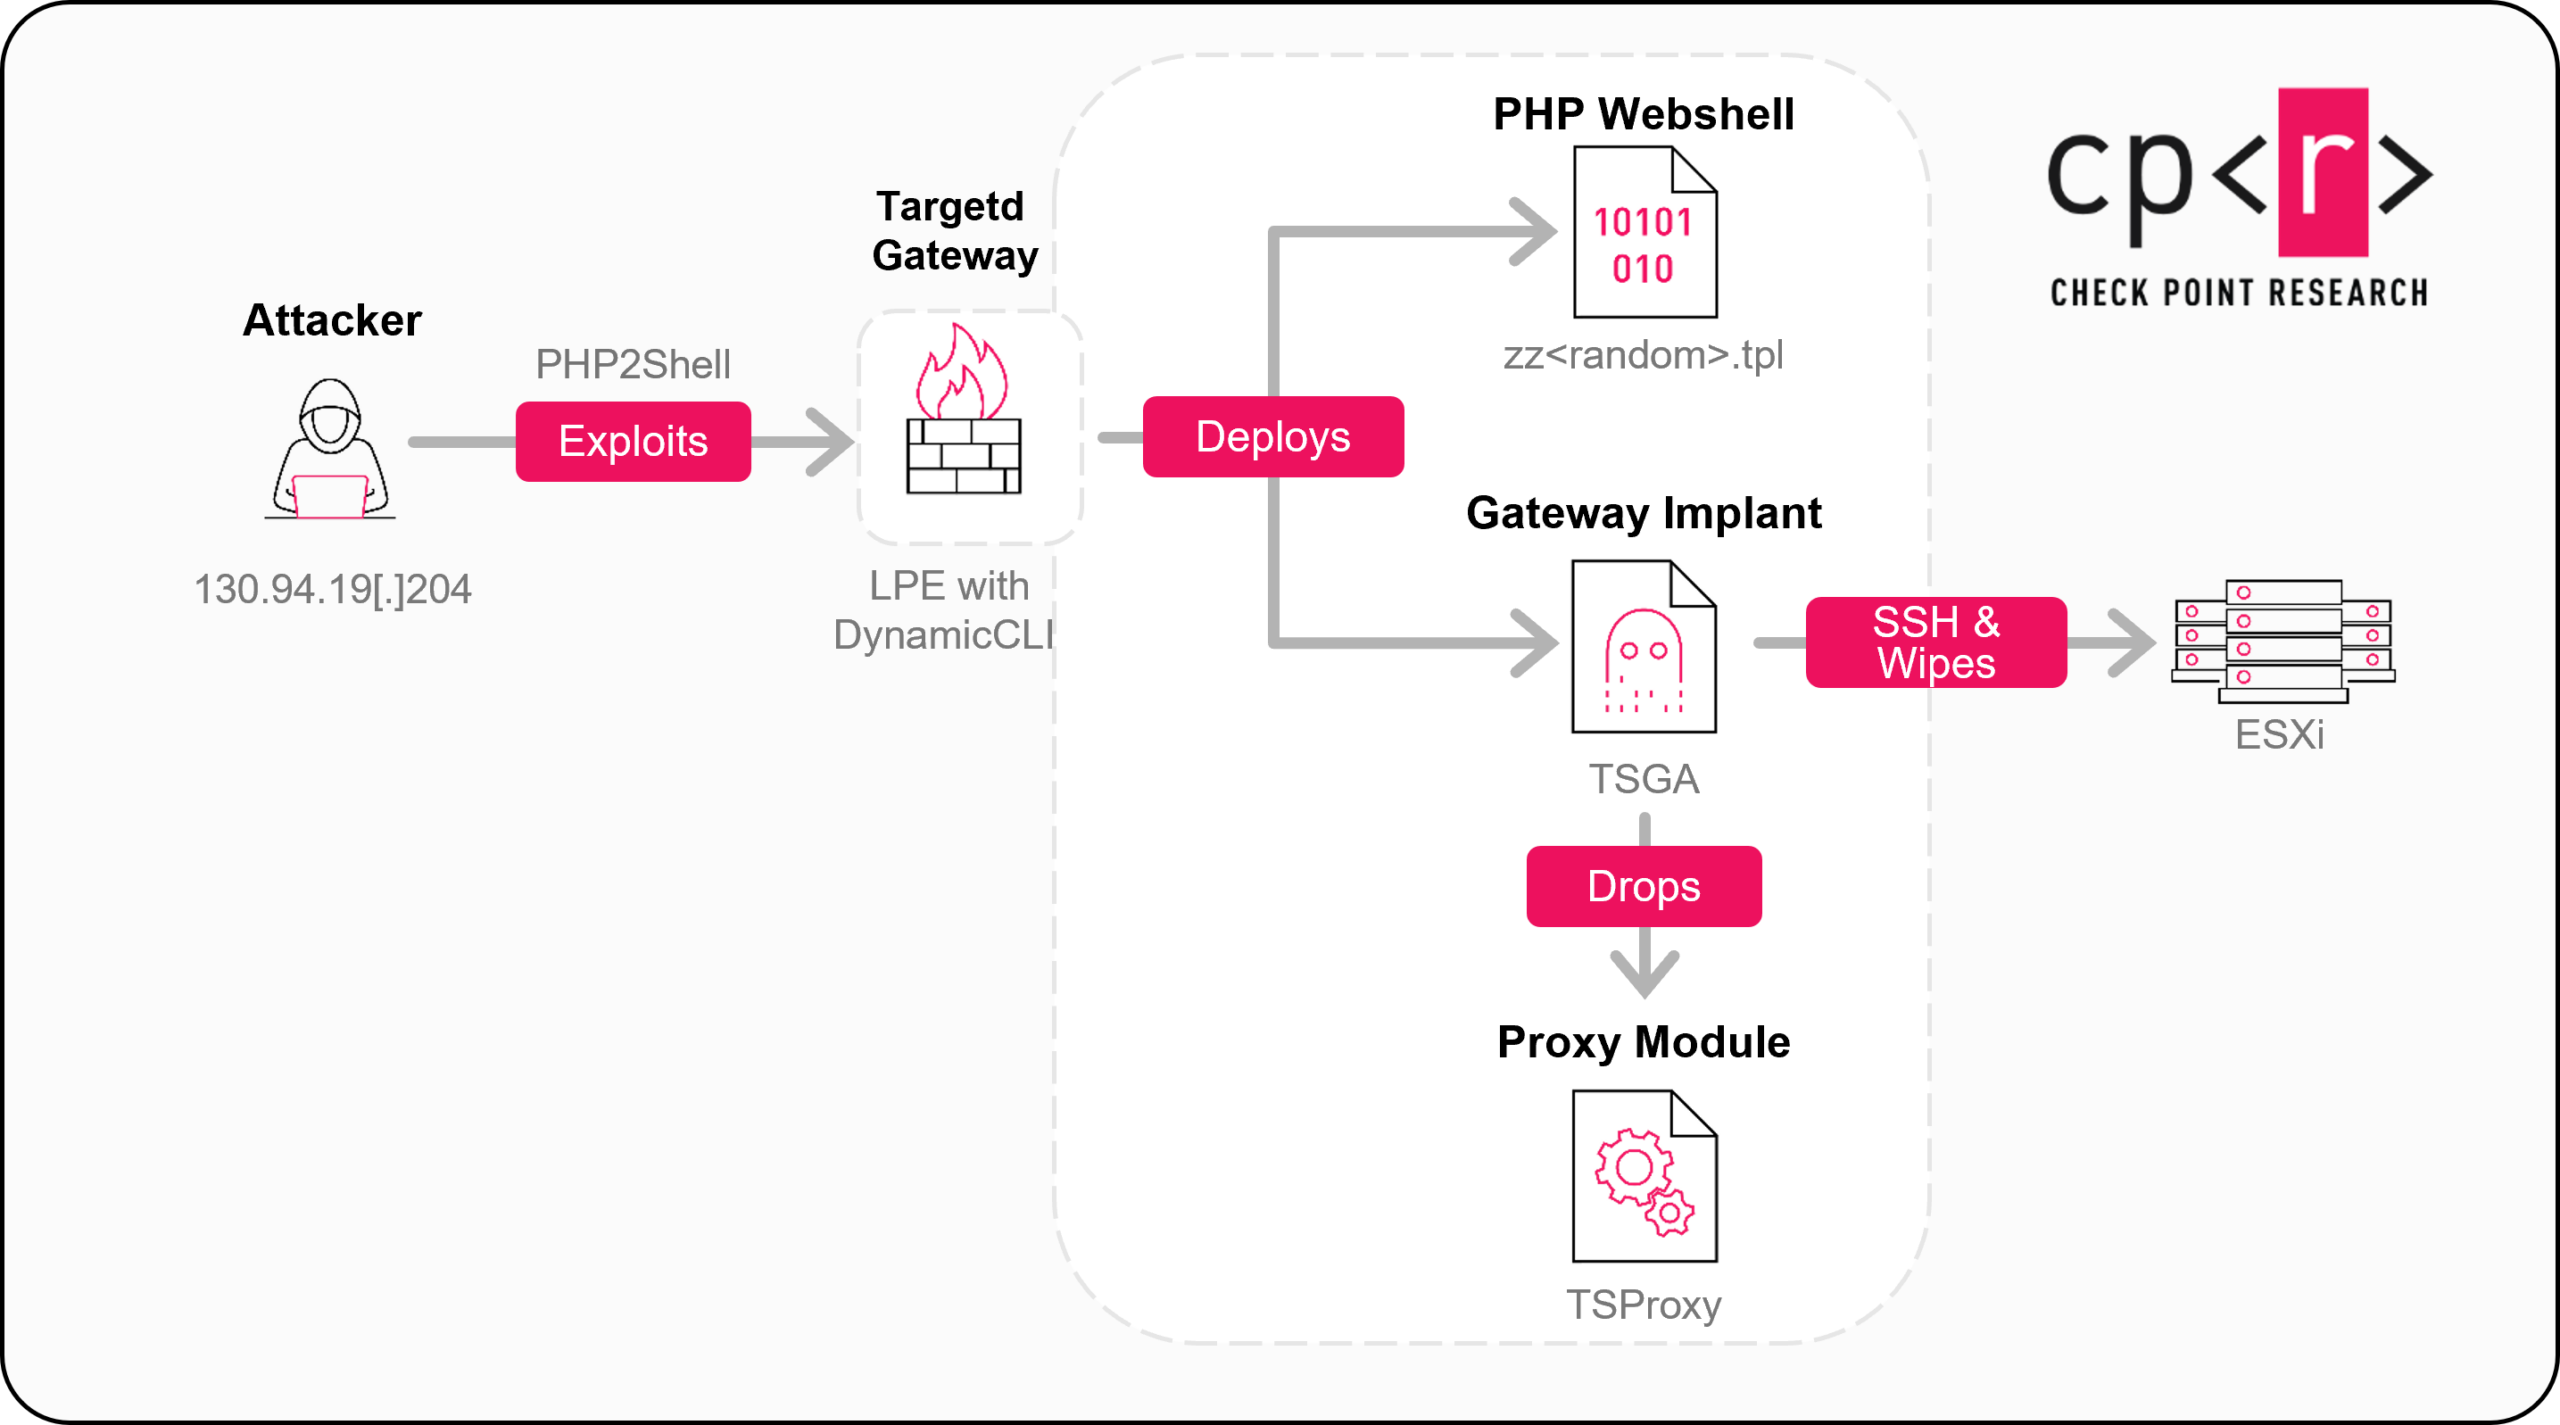
Key findings Introduction We have now confirmed that, in late October 2026, approximately one week after a security fix became available, activity originating from 130.94.19[.]204 targeted Israeli organizations through vulnerable Mobile Access portals on Check Point Security…
VulnerabilidadesFiltraciones de datos
Google Cloud informó que las máquinas virtuales con chips AMD Turin presentan tres fallos de seguridad que podrían permitir la filtración de datos. Para solucionarlo, los usuarios deben instalar el parche del sistema operativo y reiniciar la instancia mediante un proceso de…
Google fixed 83 flaws with a new Chrome 157 release, and Mozilla addressed 99 bugs in Firefox 160.
Herramientas e investigaciónMalware
Using thousands of hijacked accounts, the wfx-loot campaign planted a CI secret stealer that ran in over 1,800 GitHub repositories.
Police in nine countries, working with Europol, took down servers behind the Gootloader, CastleRAT and StealC malware operations this week and recovered more than 6 million credentials stolen from infected computers. Europol announced the action as the latest round of Operation…
Romania's intelligence agency said it stopped a cyber-espionage campaign by Russian state-linked hackers before the group exfiltrated sensitive data.
The company plans to accelerate product development, hire new talent, expand its US presence, and enter new markets.
The ongoing campaign targeting ConnectWise ScreenConnect deployments involves the exploitation of a now-patched critical security flaw in the remote access software, and not a new vulnerability, it has emerged. Blackpoint Cyber's Adversary Pursuit Group (APG), which shared the…
Ciberataques y APTIA y seguridad
Suspected Kazakhstan-linked hackers used an artificial intelligence agent to help spy on Central Asian governments, steal sensitive documents and infiltrate critical infrastructure networks, according to new research.
Palo Alto Networks ha revelado una vulnerabilidad de ejecución remota de código (RCE) en el software PAN-OS que se ejecuta en Panorama (identificada como CVE-2026-0330). Este fallo permite que un administrador autenticado con acceso a la red ejecute código arbitrario con…
MongoDB ha solucionado un fallo crítico (CVE-2026-118383) que permitía a un atacante remoto, sin necesidad de iniciar sesión, provocar la caída de un servidor de base de datos mediante el envío de solo dos solicitudes de ping. Esta vulnerabilidad, situada en el código de…